
FBI: TeamPCP Compromised Dev Tools to Steal Cloud Credentials
FBI says TeamPCP poisoned trusted developer tools to steal cloud credentials, spread malware through software updates, and extort victims.
FBI says TeamPCP poisoned trusted developer tools to steal cloud credentials, spread malware through software updates, and extort victims.
The network allegedly washed proceeds from ransomware and investment fraud through a web of exchanges and mixers.
The attack encrypted clinical systems across 14 facilities, forcing staff to revert to paper records and divert emergency patients.
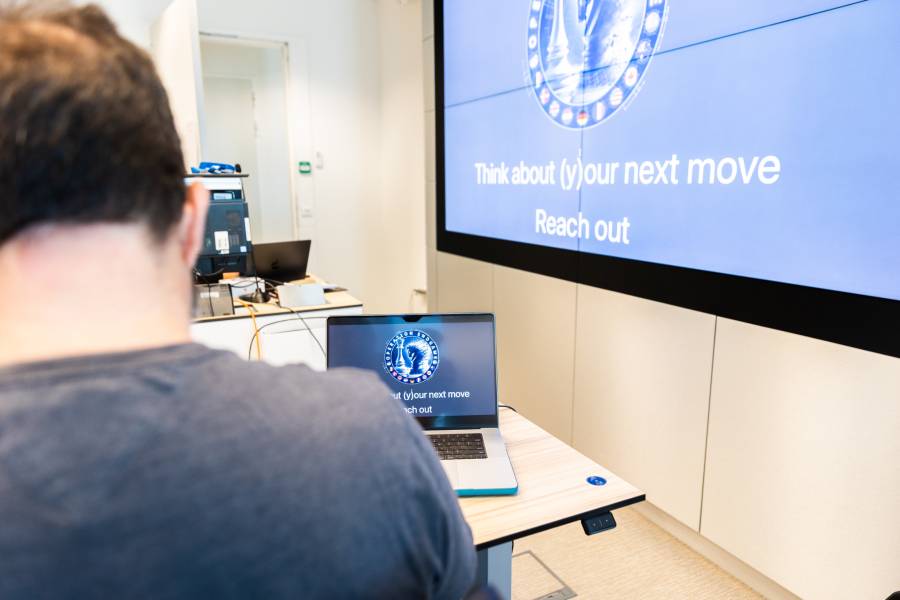
Europol together with partners from across the globe today announces a landmark blow to cybercriminal networks as part of Operation Endgame, a sweeping international operation targeting the criminal infrastructure behind ransomware and malware like SocGholish, Amadey, and…
Malicious code slipped into a widely used open-source package harvested environment variables and cloud credentials from build servers.
Campus Recruiting vulnerability exposed student information, and Audit Tracking Management System vulnerability exposed confidential internal audit data.
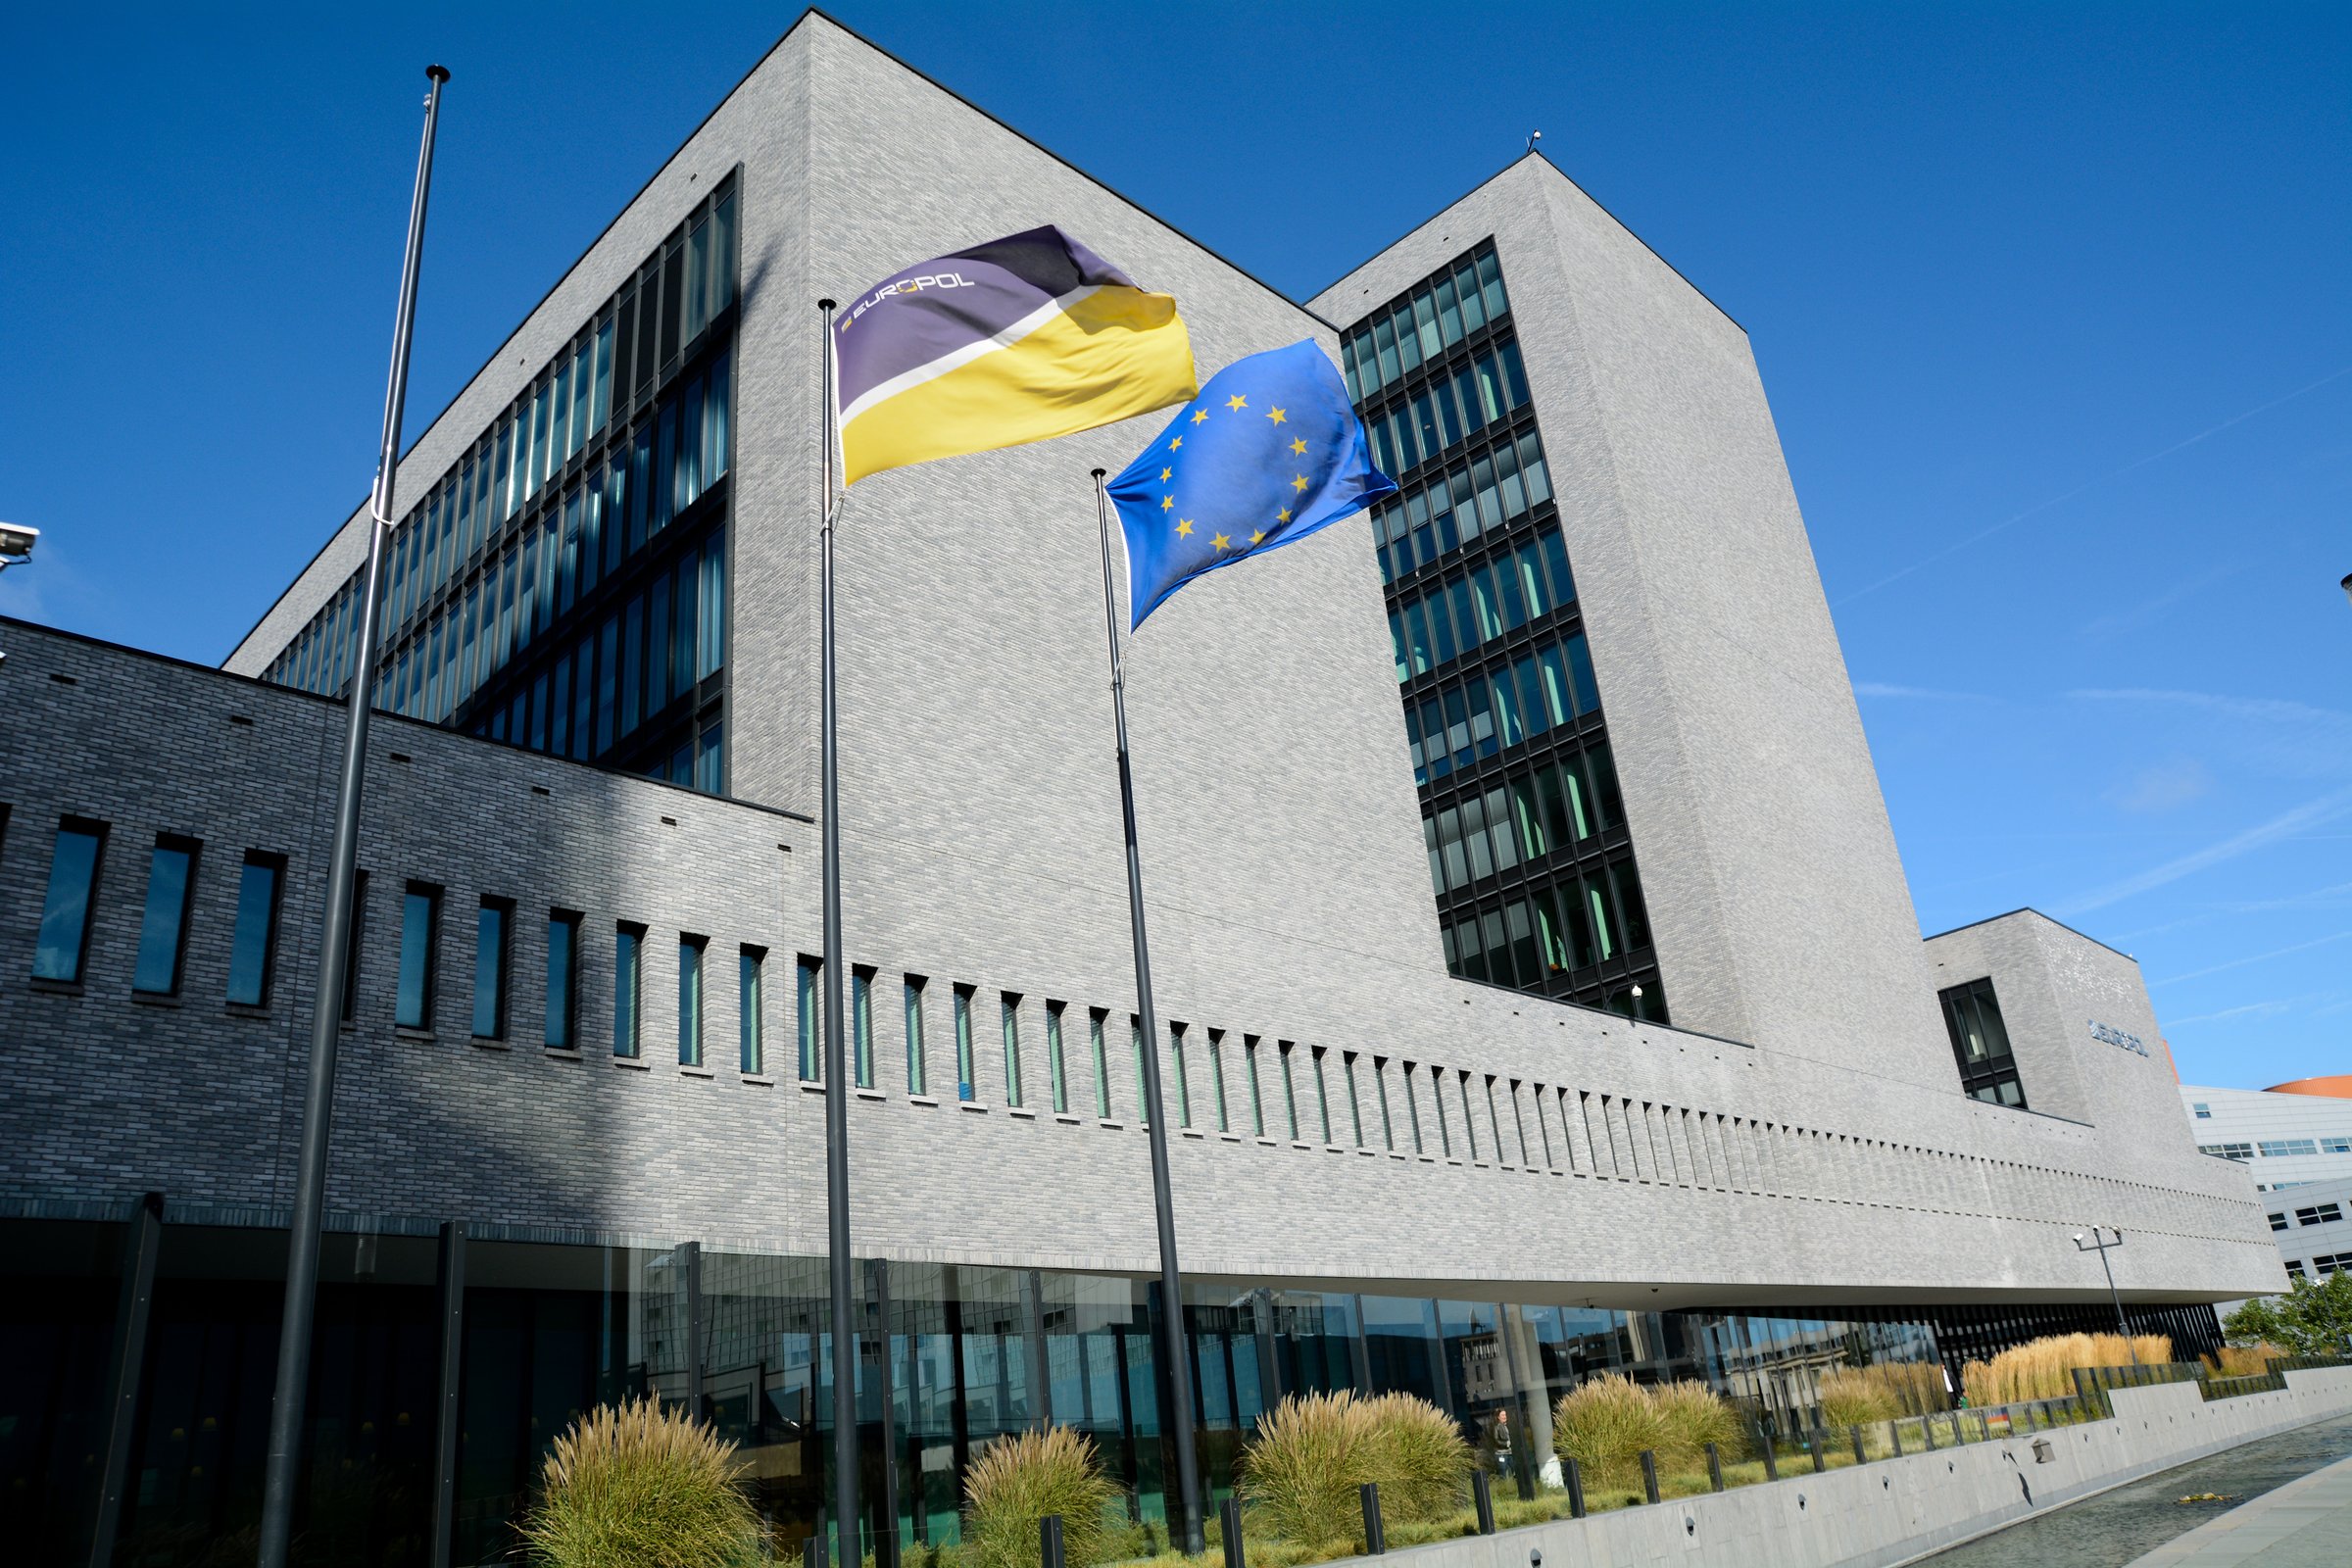
A new investigation lays bare the enormity of Europol’s rogue tactics: the agency maintained a ‘shadow IT environment’ parallel to their official databases. Keeping a second set of books is a mob classic to hide from scrutiny. Europol’s case was no different: the parallel…
The marketplace facilitated over $180 million in sales of stolen data, drugs and hacking tools before its infrastructure was seized.
Billions of login attempts fueled by recycled passwords led to account takeovers, loyalty-point theft and fraudulent purchases.
Fraudsters are cloning executive voices to authorize urgent wire transfers, with losses already exceeding $200 million globally.
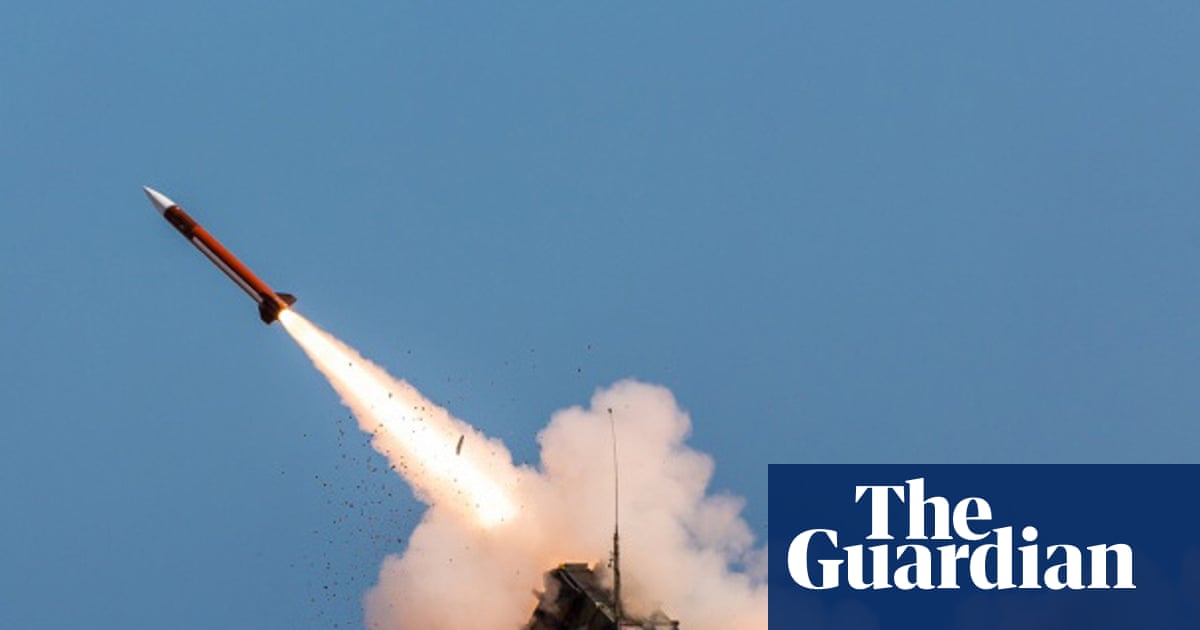
Countries that rely on US-made air defence system feel increasingly exposed as interceptor supplies dwindle
Coverage of: The FBI's Kinetic Cyber Range